Platform
Audit and compliance
Controls built into the workflow — tenant scoping, RBAC, MFA, OIDC, HIPAA profile with BAA, append-only audit trail, and retention configuration.
Controls in the product today
These controls are live for production tenants and regulated environments.
| Control | Status | Notes |
|---|---|---|
| Tenant scoping on tenant-owned records | ✅ Live | Every document, envelope, and customer record is isolated to its tenant |
| Role-based access control (RBAC) | ✅ Live | ~60 named permissions; staff access gated per capability |
| Multi-factor authentication (MFA) | ✅ Live | TOTP-based; enforced per user account |
| OIDC staff sign-in | ✅ Live | Staff can sign in via OIDC provider; no password stored |
| Password policy on credential changes | ✅ Live | Platform-enforced on all password create/change paths |
| Allowed-origins control per tenant | ✅ Live | Restrict embed and API to approved origins |
| Append-only audit trail with correlation IDs | ✅ Live | Hash-chained event log; every envelope transition recorded |
| Encryption at rest for stored files | ✅ Live | Documents and audit records encrypted at rest |
| HIPAA profile with BAA | ✅ Live | Requires tenant-level configuration; contact us to enable |
| Two-person PHI deletion gate | ✅ Live | Enforced when HIPAA profile is active |
| GDPR subject-access export | ✅ Live | Export all data for a data subject on request |
| Retention settings per tenant | ✅ Live | Configure document lifecycle and deletion policy |
| Disclosure consent text on signer path | ✅ Live | Configurable text shown before signing begins |
| Certificate of completion | ✅ Live | Generated per envelope; includes signing event summary |
| Qualified signatures (QES) | ✅ Live | Available for supported jurisdictions and signature profiles |
| EU data residency | ✅ Live | Available for eligible plans and regulated workflows |
| SAML single sign-on | ✅ Live | Available for enterprise identity provider configurations |
| SOC 2 report | ✅ Live | Available through procurement and security review channels |
Control evidence is shared through trust and procurement workflows.
Common questions
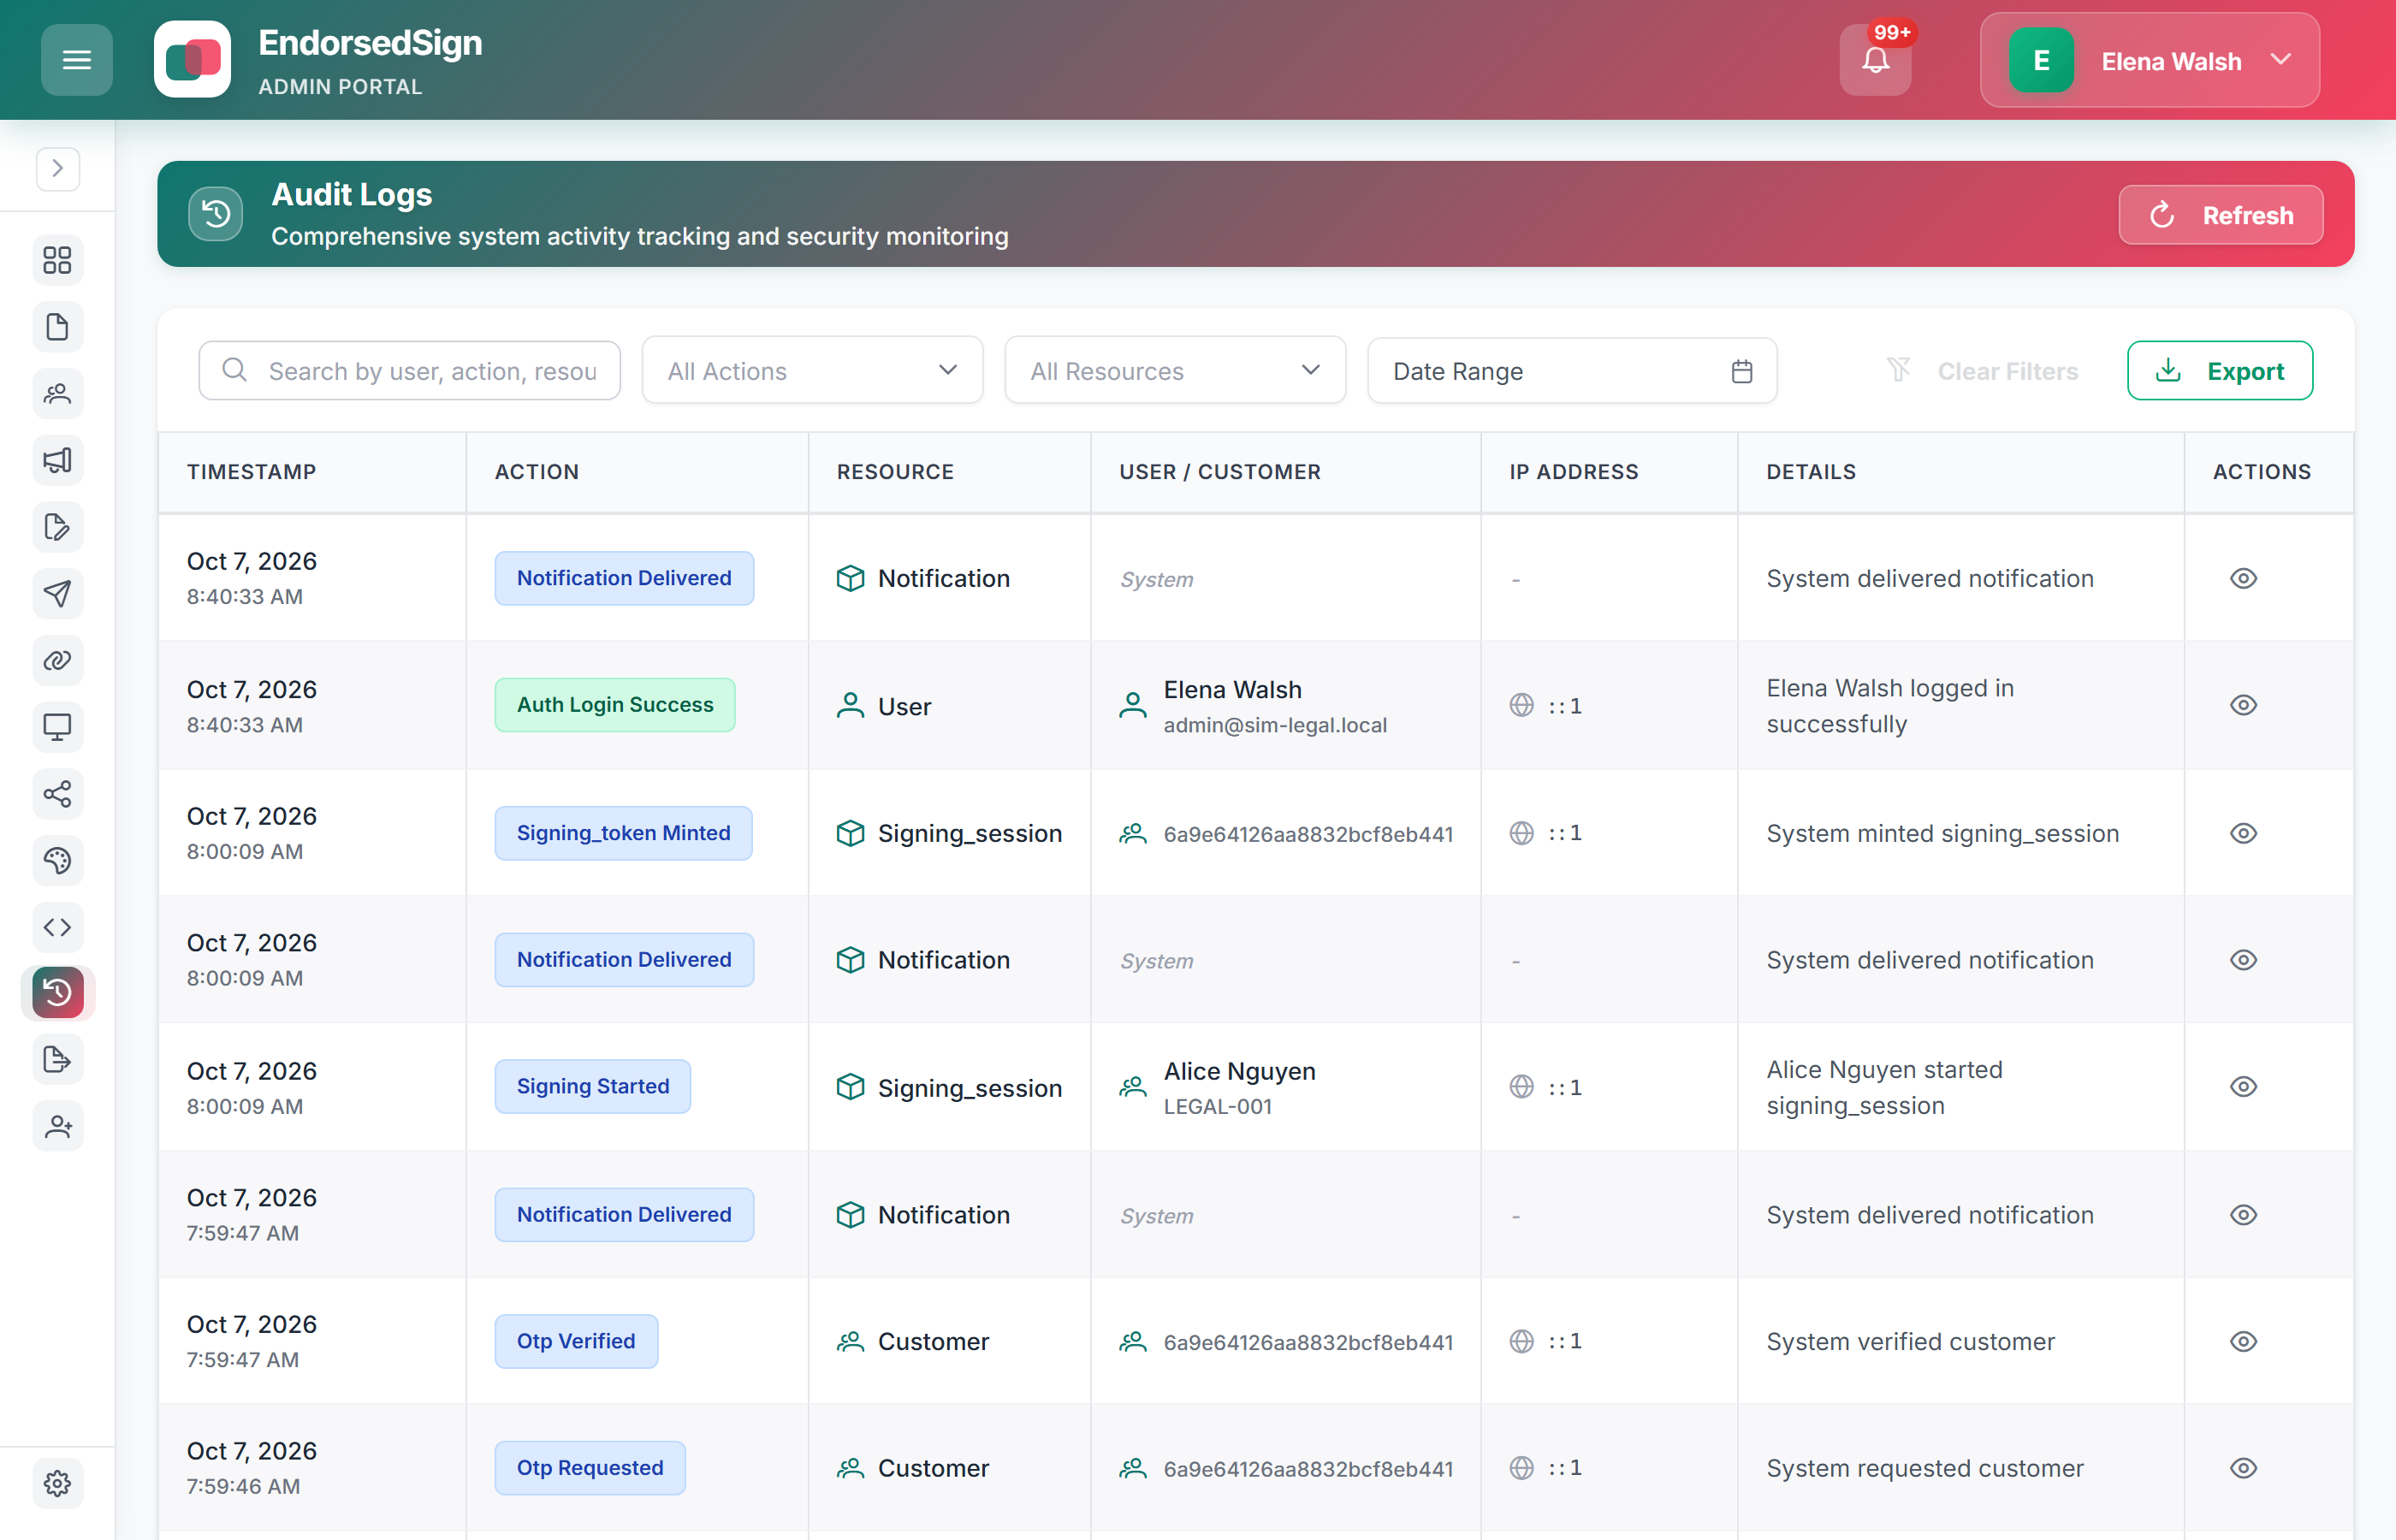
The audit trail in the admin portal
Every signing and administrative action is recorded with timestamp, actor, resource, and IP. The table below is live data from a demo tenant.
Review the full controls list in context
The security and compliance pages describe current controls and where to request supporting evidence.