IT and security teams
One signing vendor to review — explicit tenant boundaries, RBAC, MFA, OIDC, origin controls, and an auditable event chain on every action.
Named RBAC permissions
Granular role control, not binary admin/user
SSO staff sign-in
No password stored for staff accounts
Hash-chained audit trail
Read-only; no role can edit or delete events
Data isolation on every record
No cross-tenant data access by design
Security controls — current state
These controls are live for production tenants. We state what exists and how it is governed.
| Control category | Capability | Status |
|---|---|---|
| Access control | Role-based permissions (~60 named permissions) | ✅ Live |
| Access control | MFA (TOTP) on all staff accounts | ✅ Live |
| Access control | OIDC staff sign-in (no password stored) | ✅ Live |
| Access control | Password policy on credential changes | ✅ Live |
| Data isolation | Tenant scoping on all records | ✅ Live |
| Data isolation | Allowed-origins control per tenant | ✅ Live |
| Data isolation | Encryption at rest for stored files | ✅ Live |
| Audit | Hash-chained append-only audit trail | ✅ Live |
| Audit | Correlation IDs on all API requests | ✅ Live |
| Compliance | HIPAA profile + BAA (opt-in per tenant) | ✅ Live |
| Compliance | GDPR subject-access export | ✅ Live |
| Compliance | Two-person PHI deletion gate | ✅ Live |
| Compliance | SOC 2 audit report (independent) | ✅ Live |
| Compliance | SAML SSO | ✅ Live |
| Compliance | EU data residency | ✅ Live |
Capability evidence is available through trust and procurement workflows.
Common questions from IT and security teams
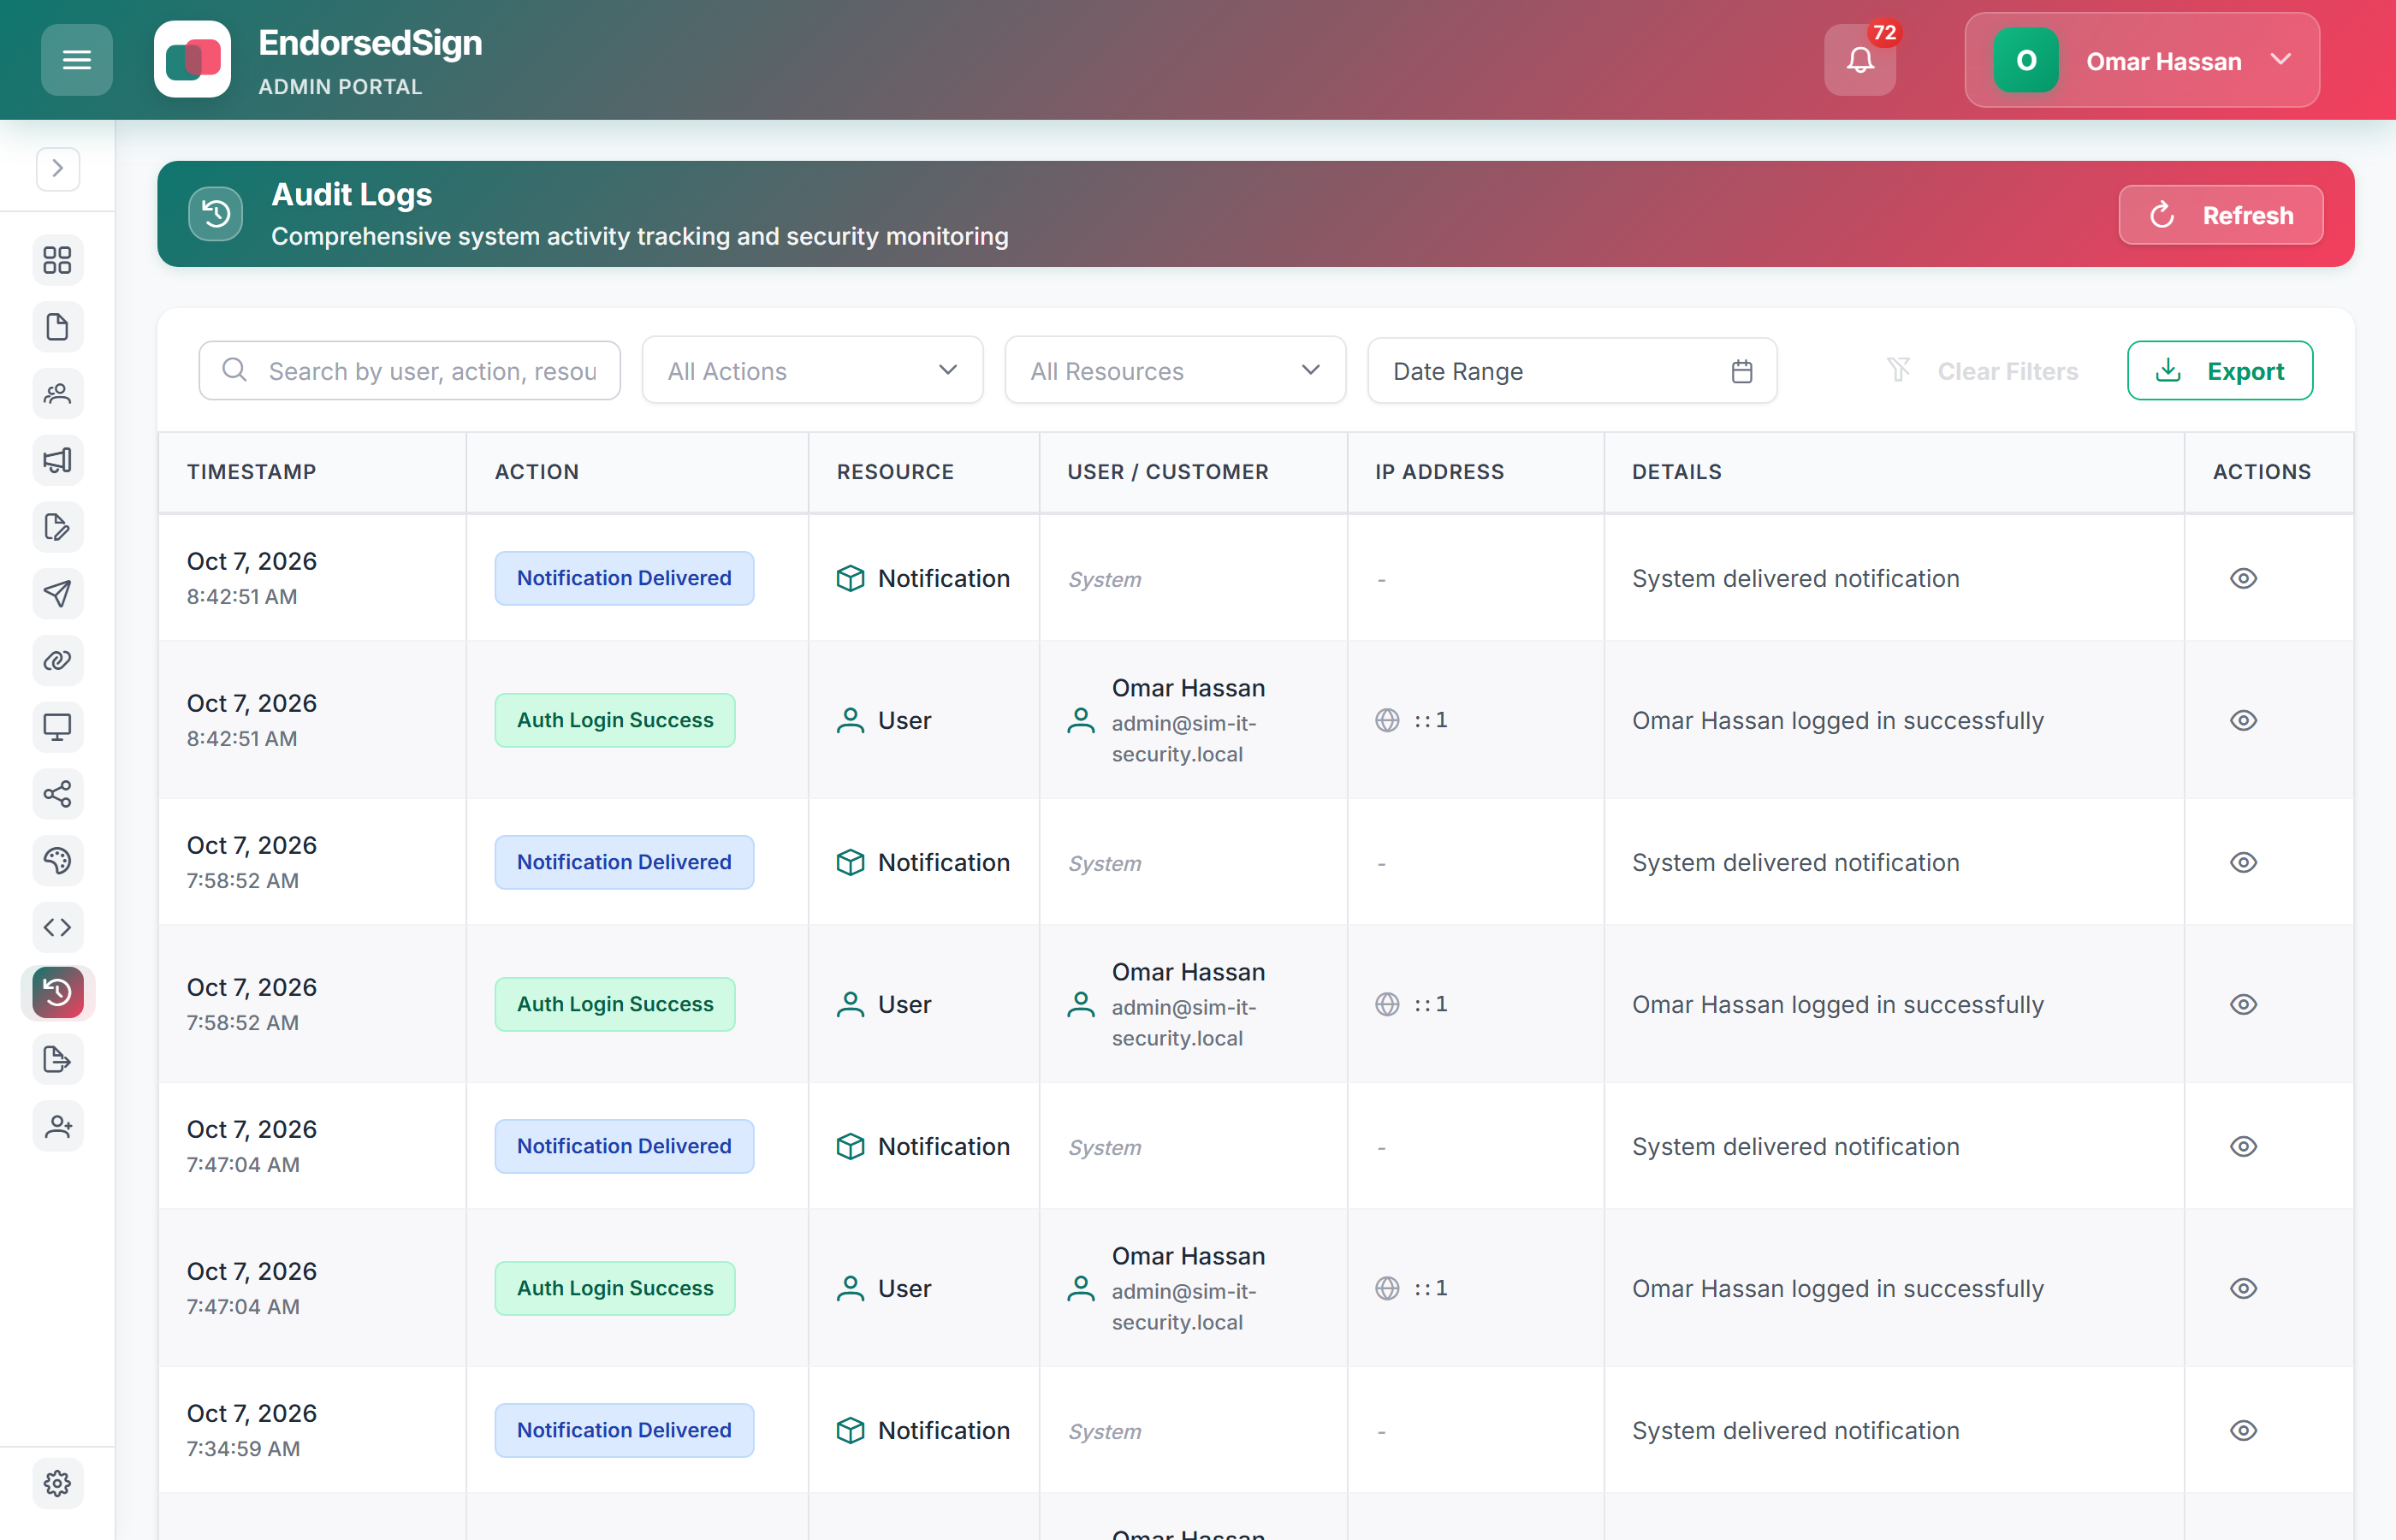
Audit trail — what IT and security teams see
Every access and signing event is recorded with actor, resource, IP, and correlation ID. The log is read-only — no role can edit or delete events. Exportable as CSV for SIEM ingestion.
Review the security posture and request access
The security and compliance pages list current controls. Start a trial or request evidence to review the full vendor security documentation.